About Bugb
Built by security engineers, for security engineers.
We model threats as code, test them as code, and hand developers evidence they can act on. Our foundations are open source. Bravos runs them as one loop, for a single developer, a team or an enterprise.
Security work should feel like
pair-programming with an expert.
We already know where the world's doors are. We teach specialized AI agents to make and test the keys. Our security control plane thinks like an attacker and works like an engineer, proving real risk and fixing it fast.
Three products, one loop. GuardLink writes the threat model into the code. Cert-X-Gen runs the probes. Bravos drives both, and writes what it confirms back into the source.
Security First
Security should be proactive, not reactive. Our AI agents work continuously to find and validate threats before they become breaches.
Open Source
Cert-X-Gen and Guardlink are fully open source. We believe transparency builds trust, inspect, contribute, and verify.
AI-Native
Built from day one with LLM reasoning at the core. Not legacy scanners with a chatbot. Every product thinks, plans, and validates.
The people behind Bugb.
Four of us lead the company. The GitHub handles are the accounts we commit to GuardLink and Cert-X-Gen from.
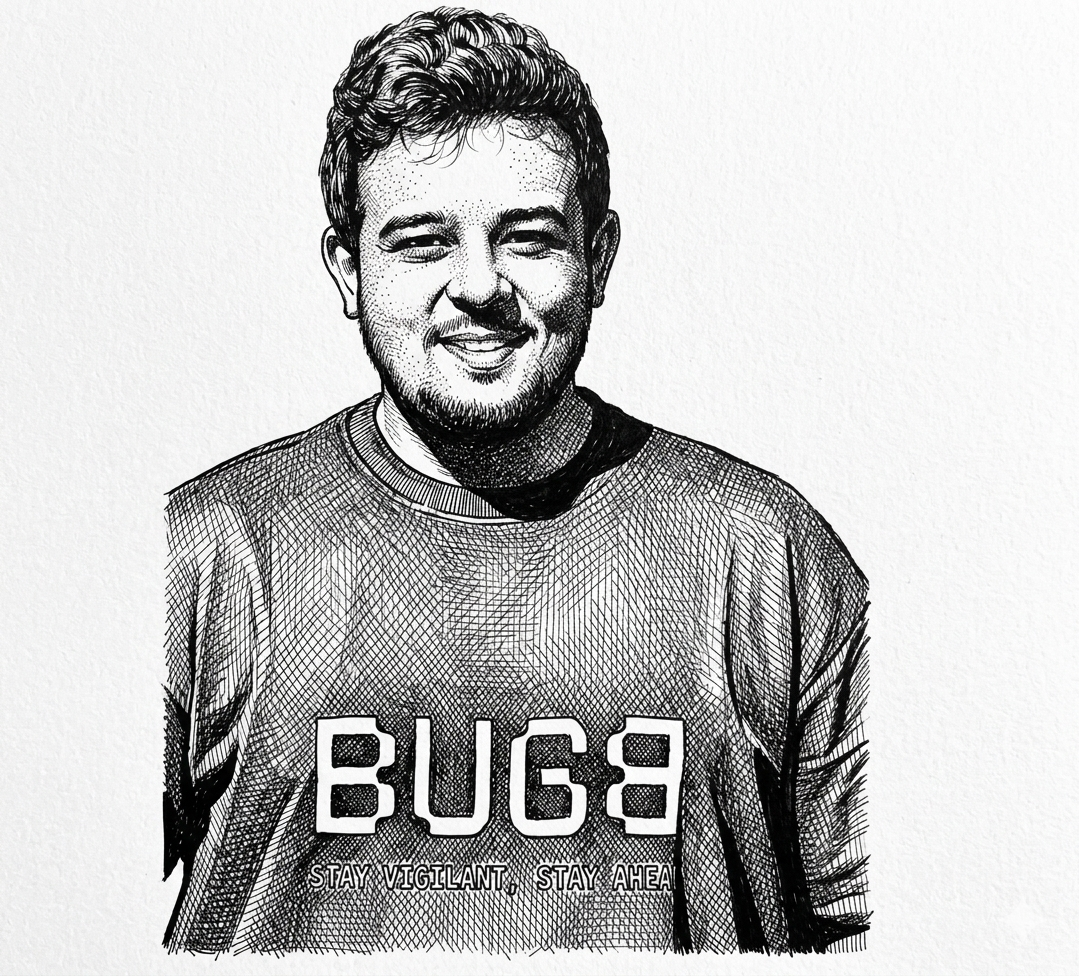
Shahid Hakimji
Co-Founder, CEO & Director
Decade of experience in cybersecurity and solutions architecture. Ex-Principal Product Security Engineer at Dell and JumpCloud.
Credited for CVE-2024-50562 and CVE-2023-27290
Animesh Srivastava
Co-Founder & CTO
Ex-Lead AI Engineer at Cisco. IISc Alumni. Leveraged big data, ML, and LLMs to solve enterprise-scale security challenges.
Ashish Shroff
Co-Founder & COO
Ex-Senior Manager at Morgan Stanley. 10+ years in software engineering and security. Previously led engineering teams at Philips.
Shifa Miyaji
Director, Head of Marketing
Marketing and communications specialist with wealth of experience across diverse industries.
CVEs we reported.
Public CVE records where the vendor advisory or our own write-up credits a Bugb researcher. Scores are the vendor's CVSS v3 base score.
CVE-2024-50562
Fortinet FortiOS SSL-VPN
Insufficient session expiration: a logged-out SSL-VPN cookie could be replayed to regain portal access.
CVE-2023-27290
IBM Observability with Instana
Docker-based datastores did not require authentication, giving network attackers read and write access.
How we got here
From a research idea to a product teams can buy, in the order it happened.
2022
The idea
Moved from generic scanning to finding the applications a specific vulnerability actually affects.
Late 2022
Research published
Published in IEEE and presented at WHDCON in Qatar.
Mar 2023
First CVE
Reported CVE-2023-27290 to IBM (CVSS 9.1).
Nov 2023
Cert-X-Gen v1
Built the first version of Cert-X-Gen, our pentest-as-code engine.
Mar 2024
Incorporated
Registered as Bugb Technologies Private Limited.
Aug 2024
First client
Started our first client engagement.
Oct 2026
Bravos available
Bravos licences went on sale, per developer or for a team, through account.bugb.io.